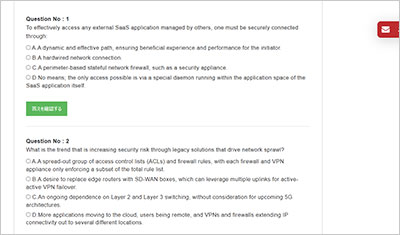
サンプル問題 1: How is policy enforcement in Zero Trust done?
A: As a binary decision of allow or block.
B: Without trust, for example Zero Trust.
C: Conditionally, in that an allow or a block will have additional controls assigned, for example Allow and isolate, or Block and Deceive.
D: At the network level, by source I
正解:C
Explanation: In Zero Trust architecture, policy enforcement is conditional and context-based, not limited to a simple binary allow-or-block model. Zscaler’s reference architectures explain that policy is evaluated using the full user context, including identity, device posture, location, group membership, and other conditions. Access decisions are therefore based on whether specific policy conditions are true, rather than only on static network attributes such as source IP address. For example, the same authenticated user may be allowed access from a managed device at headquarters but denied from an airport, even with the same credentials. Zscaler documentation also shows that Zero Trust policy can go beyond simple pass or deny outcomes by applying additional controls. In DNS Security and Control, requests can be allowed, blocked, or modified. In ZIA policy development, Cloud App controls allow more granular outcomes than standard allow/block, such as restricting specific actions, applying quotas, or controlling what a user can do inside an application. This reflects the Zero Trust principle that enforcement is adaptive, granular, and tied to business and security context rather than network location alone.
サンプル問題 2: A Zero Trust network can be:
A: Located anywhere.
B: Built on IPv4 or IPv6.
C: Built using VPN concentrators.
D: Located anywhere and built on IPv4 or IPv6.
正解:D
Explanation: The correct answer is D. Located anywhere and built on IPv4 or IPv6. In Zero Trust architecture, the network and application access model is not tied to a specific physical location, branch, or data center. Zscaler’s Zero Trust guidance emphasizes that users, devices, and applications can be securely connected in any location, which is a core shift away from legacy perimeter-based designs. The architecture is also described as IP independent, meaning policy and access decisions are not fundamentally anchored to traditional network constructs such as fixed addressing or trusted subnets. This is why Zero Trust can operate across modern environments regardless of where workloads reside. The option about VPN concentrators is incorrect because VPN-based architecture is associated with legacy remote-access models that extend network trust and expose services differently from Zero Trust. In contrast, Zero Trust reduces implicit trust, avoids broad network-level access, and focuses on secure, application-aware connectivity. Therefore, the most complete and accurate answer is that a Zero Trust network can be located anywhere and built on IPv4 or IPv6, rather than being limited to a legacy transport or perimeter model.
サンプル問題 3: How are services protected in a legacy scenario when they are discoverable on the public Internet? (Select all that apply)
A: Establishing a DMZ that would include multiple products and services.
B: Dynamic Application Security Testing (DAST).
C: A large security stack including appliances that handle functions like global load balancing, firewalling, DDoS, and more.
D: A web application firewall (WAF) for protecting against DDoS and other botnet style attacks.
正解:A, C, D
Explanation: The correct answers are A, C, and D. In a legacy architecture, applications that are exposed and discoverable on the public Internet are usually protected by building a DMZ (demilitarized zone) and placing multiple security technologies in front of the service. This commonly includes a large security stack made up of separate appliances or services for functions such as load balancing, firewalling, distributed denial-of-service (DDoS) protection, and related edge security controls. A web application firewall (WAF) is also a standard protective element in these public-facing designs because it adds inspection and protection for web-based attack patterns and internet-originated abuse. Option B, DAST, is not a correct answer because Dynamic Application Security Testing is a testing and assessment method, not a live architectural protection control that sits inline to defend exposed services in production. Zero Trust architecture contrasts with this legacy model by removing direct public discoverability and reducing dependence on a complex exposed edge stack. Instead of defending openly exposed applications with layered perimeter tools, Zero Trust aims to make applications less discoverable and access more identity- and policy-driven.
Zscaler ZTCA試験準備をしていますか?それとも自分は全部できそうです。復習する必要がないと思いますか?それとも自分は何もできないような気がします。どうすればいいでしょうか?実は、この問題を解決するのは難しくないです。勉強者がやるべきのは分解分析をマスターすることです。ここではZTCA問題集を使って学習中の課題を確認し、知識を整理してZscaler Zero Trust Cyber Associate試験の準備を進めます。
その次に、非常規の試験ポイントのテーマは多すぎてこだわる必要はなくて、重要な試験点のテーマはきっと知識の点をわかります。特にZscaler Zero Trust Cyber Associate試験は試験資料ポイントが多いです。一つの問題は知識ポイントだけではなく、復習する時はまとめをマスターして、記憶を分類します。知識ポイントが覚えていないか、間違えていないかのために点数をなくしてはいけません。