サンプル問題 1: What are two benefits of a Nozomi integration with FortiNAC? (Choose two.)
A: Enhanced point of connection details
B: Direct VLAN assignment
C: Adapter consolidation for multi-adapter hosts
D: Importation and classification of hosts
正解:C, D
Explanation: The two benefits of a Nozomi integration with FortiNAC are enhanced point of connection details and importation and classification of hosts. Enhanced point of connection details allows for the identification and separation of traffic from multiple points of connection, such as Wi-Fi, wired, cellular, and VPN. Importation and classification of hosts allows for the automated importing and classification of host and device information into FortiNAC. This allows for better visibility and control of the network
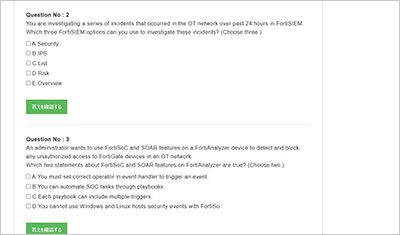
サンプル問題 2: Which three criteria can a FortiGate device use to look for a matching firewall policy to process traffic? (Choose three.)
A: Services defined in the firewall policy.
B: Source defined as internet services in the firewall policy
C: Lowest to highest policy ID number
D: Destination defined as internet services in the firewall policy
E: Highest to lowest priority defined in the firewall policy
正解:A, B, D
Explanation: Services defined in the firewall policy - This involves checking the traffic against service definitions such as HTTP, HTTPS, SSH, etc., specified in the policy. Source defined as internet services in the traffic policy - This criterion involves checking whether the source of the traffic is defined as internet services within the policy settings. Destination defined as internet been services in the firewall policy - This includes verifying if the traffic's destination matches any of the internet services specified in the policy.
サンプル問題 3: Which three Fortinet products can be used for device identification in an OT industrial control system (ICS)? (Choose three.)
A: FortiNAC
B: FortiManager
C: FortiAnalyzer
D: FortiSIEM
E: FortiGate
正解:A, D, E
Explanation: A) FortiNAC - FortiNAC is a network access control solution that provides visibility and control over network devices. It can identify devices, enforce access policies, and automate threat response. D) FortiSIEM - FortiSIEM is a security information and event management solution that can collect and analyze data from multiple sources, including network devices and servers. It can help identify potential security threats, as well as monitor compliance with security policies and regulations. E) FortiAnalyzer - FortiAnalyzer is a central logging and reporting solution that collects and analyzes data from multiple sources, including FortiNAC and FortiSIEM. It can provide insights into network activity and help identify anomalies or security threats. Reference: Fortinet NSE 7 - OT Security 6.4 Study Guide, Chapter 4: OT Security Devices, page 4-20.
Fortinet NSE6_OTS_AR-7.6試験の準備に向けた復習資料としてNSE6_OTS_AR-7.6問題集を提供しています。Fortinet NSE 6 - OT Security 7.6 Architect試験の主要な知識ポイントをカバーしています。ページ上部の「NSE6_OTS_AR-7.6 試験を開始する」ボタンからオンライン無料サンプル問題を確認できます。
NSE6_OTS_AR-7.6問題集の収録内容と更新状況はどうなっていますか?
答え:現在提供されているNSE6_OTS_AR-7.6問題集には、NSE6_OTS_AR-7.6試験対策に向けた全69問の練習問題と解答が収録されています。Fortinet NSE 6 - OT Security 7.6 Architect試験に向けた復習に利用できます。