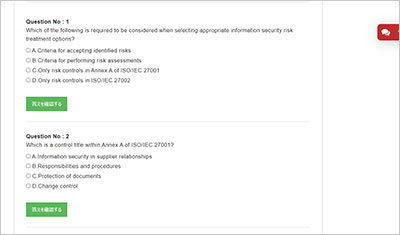
サンプル問題 1: Which statement is a factor that will influence the implementation of the information security management system?
A: The ISMS will be separate from the organization's overall management structure
B: The ISMS will encompass all controls specified within ISO/IEC 27001
C: The ISMS will be scaled to the controls according to the needs of the organization
D: The ISMS will be operated as an independent process within the organization
正解:C
Explanation: ISO/IEC 27001 makes clear that the ISMS is intended to be tailored to the organization. The standard states: “This document also includes requirements for the assessment and treatment of information security risks tailored to the needs of the organization. The requirements set out in this document are generic and are intended to be applicable to all organizations regardless of type, size or nature.” This means implementation is scaled based on each organization’s risk, context, and needs, not a fixed one-size-fits-all set of activities or controls. Clause 6.1.3 further reinforces that control selection is flexible and risk-driven: “Organizations can design controls as required or identify them from any source,” and “Annex A contains a list of possible information security controls… The information security controls listed in Annex A are not exhaustive and additional information security controls can be included if needed.” Together, these extracts verify that the ISMS implementation is influenced by and scaled to the organization’s needs and selected controls, not separated from management processes (A, D) nor mandated to include “all controls” (B)
サンプル問題 2: Which factor is required to be determined when understanding the organization and its context?
A: Internal issues affecting the purpose of the ISMS
B: The information security objectives relevant to the ISMS
C: The processes that will be required to operate the ISMS
D: The ISO/IEC 27001 clauses which apply to the management system
正解:A
Explanation: Clause 4.1 specifies exactly what must be determined when establishing context: “The organization shall determine external and internal issues that are relevant to its purpose and that affect its ability to achieve the intended outcome(s) of its information security management system.” This requirement is about understanding internal and external issues (e.g., culture, capabilities, regulatory environment) that influence the ISMS’s effectiveness. Objectives (option B) are addressed later in Clause 6.2; processes (option C) are addressed in Clause 4.4 and operational planning; and “which clauses apply” (option D) is not a determination step―ISO/IEC 27001’s requirements in Clauses 4C10 are not optional. Therefore, the direct, required factor per 4.1 is determining internal (and external) issues relevant to the organization’s purpose and ISMS outcomes.
サンプル問題 3: Which audit activity related to ISO/IEC 27001 may be carried out by a practitioner?
A: Conduct a surveillance audit of their own area of the organization
B: Conduct an internal audit of the organization
C: Conduct an audit of an Accredited Training Organization
D: Conduct an audit of a Certification Body
正解:B
Explanation: ISO/IEC 27001 requires internal audits and sets out how they must be conducted: “The organization shall conduct internal audits at planned intervals…” (9.2.1) and “plan, establish, implement and maintain an audit programme(s)… [and] select auditors and conduct audits that ensure objectivity and the impartiality of the audit process” (9.2.2). These extracts confirm that practitioners (internal to the organization) can conduct internal audits provided objectivity and impartiality are ensured (e.g., they do not audit their own work). Surveillance audits (option A) and audits of Accredited Training Organizations or Certification Bodies (options C, D) are third-party activities outside the remit of an internal practitioner under ISO/IEC 27001; the standard’s audit requirement is focused on the organization’s own internal audit programme. Therefore, conducting an internal audit (B) is the correct practitioner activity per Clause 9.2.
PECB ISO-IEC-27001 Foundation試験準備をしていますか?それとも自分は全部できそうです。復習する必要がないと思いますか?それとも自分は何もできないような気がします。どうすればいいでしょうか?実は、この問題を解決するのは難しくないです。勉強者がやるべきのは分解分析をマスターすることです。ここではISO-IEC-27001 Foundation問題集を使って学習中の課題を確認し、知識を整理してISO/IEC 27001 (2022) Foundation Exam試験の準備を進めます。
その次に、非常規の試験ポイントのテーマは多すぎてこだわる必要はなくて、重要な試験点のテーマはきっと知識の点をわかります。特にISO/IEC 27001 (2022) Foundation Exam試験は試験資料ポイントが多いです。一つの問題は知識ポイントだけではなく、復習する時はまとめをマスターして、記憶を分類します。知識ポイントが覚えていないか、間違えていないかのために点数をなくしてはいけません。