

GOWUKAKU|IT認定資格の最新の試験問題集(PDF版・無料サンプル問題)を提供しています
GIAC Certified Enterprise Defender 試験
最終更新日: 2026/10/10 収録内容確認済 | PDF問題集: 全 88 問収録
【仕様案内】:GCED 問題集(PDF版)は日本語版&英語版の2言語セットに対応しております(日本語版が準備中の科目は英語版を即時ダウンロードのうえ、日本語版は準備完了次第ご登録メールへ自動送付いたします)。
本ページでは問題集の無料サンプル問題を公開しており、出題形式や現在の理解度を確認することができます。
全88問を収録したPDF版は、GCED 問題集からご確認いただけます。
Question No : 1
What feature of Wireshark allows the analysis of one HTTP conversation?
正解:
Explanation:
Follow TCP Stream is a feature of Wireshark that allows the analysis of a single TCP conversation between two hosts over multiple packets. Filtering packets using tcp in the filter box will return all TCP packets, not grouping by a single TCP conversation. HTTP is TCP not UDP, so you cannot follow a HTTP stream over UDP.
Question No : 2
Before re-assigning a computer to a new employee, what data security technique does the IT department use to make sure no data is left behind by the previous user?
正解:
Question No : 3
When attempting to collect data from a suspected system compromise, which of the following should generally be collected first?
正解:
Question No : 4
A company wants to allow only company-issued devices to attach to the wired and wireless networks. Additionally, devices that are not up-to-date with OS patches need to be isolated from the rest of the network until they are updated.
Which technology standards or protocols would meet these requirements?
正解:
Question No : 5
Michael, a software engineer, added a module to a banking customer’s code. The new module deposits small amounts of money into his personal bank account. Michael has access to edit the code, but only code reviewers have the ability to commit modules to production. The code reviewers have a backlog of work, and are often willing to trust the software developers’ testing and confidence in the code.
Which technique is Michael most likely to engage to implement the malicious code?
正解:
Question No : 6
An internal host at IP address 10.10.50.100 is suspected to be communicating with a command and control whenever a user launches browser window.
What features and settings of Wireshark should be used to isolate and analyze this network traffic?
正解:
Question No : 7
Who is ultimately responsible for approving methods and controls that will reduce any potential risk to an organization?
正解:
Question No : 8
If a Cisco router is configured with the “service config” configuration statement, which of the following tools could be used by an attacker to apply a new router configuration?
正解:
Question No : 9
Which Unix administration tool is designed to monitor configuration changes to Cisco, Extreme and Foundry infrastructure devices?
正解:
Explanation:
RANCID is a Unix tool which can be used to monitor changes to the following networked devices and more: IOS, CatOS, PIX, Juniper, Foundry, HP ProCurve, Extreme.
Question No : 10
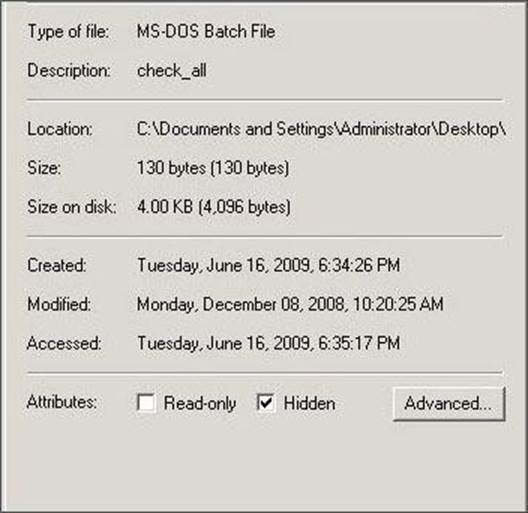
Which command tool can be used to change the read-only or hidden setting of the file in the screenshot?
正解:
Explanation:
attrib Cr or +r will remove or add the read only attribute from a file.
Question No : 11
On which layer of the OSI Reference Model does the FWSnort utility function?
正解:
Explanation:
The FWSnort utility functions as a transport layer inline IPS.
Question No : 12
Why would the pass action be used in a Snort configuration file?
正解:
Explanation:
The pass action is defined because it is sometimes easier to specify the class of data to ignore rather than the data you want to see. This can cut down the number of false positives and help keep down the size of log data. False positives occur because rules failed and indicated a threat that is really not one. They should be minimized whenever possible. The pass action causes the packet to be ignored, not passed on further. It is an active command, not a placeholder.
Question No : 13
Why might an administrator not be able to delete a file using the Windows del command without specifying additional command line switches?
正解:
Question No : 14
At the start of an investigation on a Windows system, the lead handler executes the following commands after inserting a USB drive.
What is the purpose of this command?
C:\ >dir / s / a dhsra d: \ > a: \ IRCD.txt
正解:
Explanation:
This command will create a text file on the collection media (in this case you would probably be using a USB flash drive) named IRCD.txt that should contain a recursive directory listing of all files on the desk.
Question No : 15
Which of the following attacks would use “..” notation as part of a web request to access restricted files and directories, and possibly execute code on the web server?
正解: