

GOWUKAKU|IT認定資格の最新の試験問題集(PDF版・無料サンプル問題)を提供しています
GIAC Advanced Smartphone Forensics 試験
最終更新日: 2026/10/15 収録内容確認済 | PDF問題集: 全 71 問収録
【仕様案内】:GASF 問題集(PDF版)は日本語版&英語版の2言語セットに対応しております(日本語版が準備中の科目は英語版を即時ダウンロードのうえ、日本語版は準備完了次第ご登録メールへ自動送付いたします)。
本ページでは問題集の無料サンプル問題を公開しており、出題形式や現在の理解度を確認することができます。
全71問を収録したPDF版は、GASF 問題集からご確認いただけます。
Question No : 1
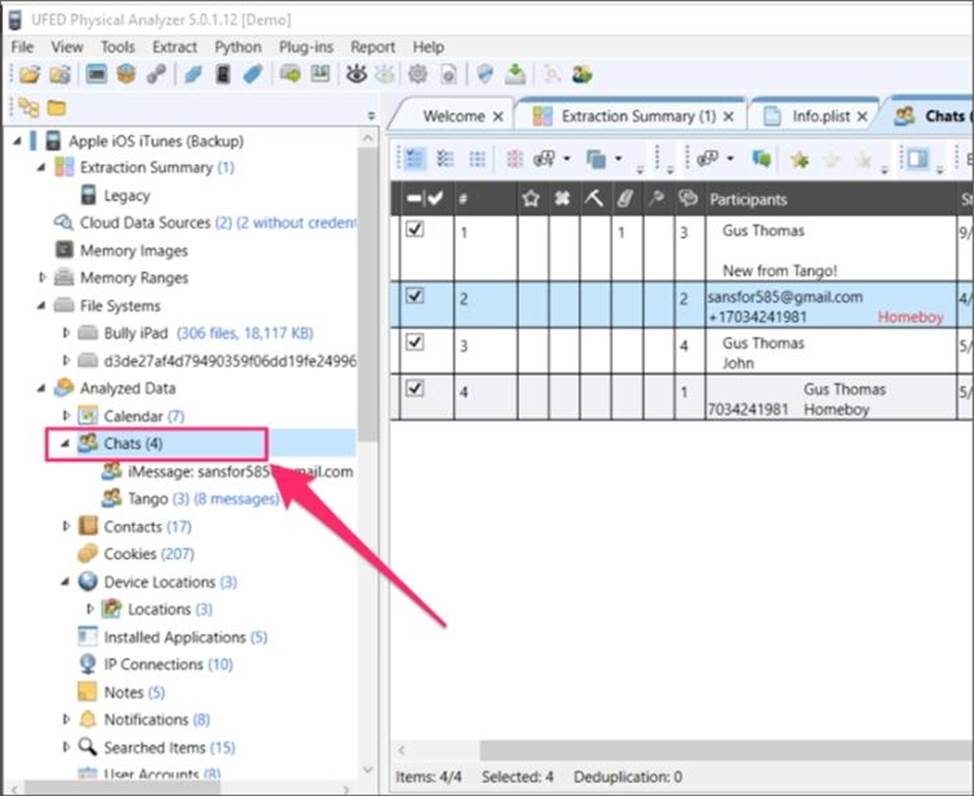
When examining the iOS device shown below the tool indicates that there are 4 chat messages recovered
正解:
Question No : 2
Which of the following is the term for the SMS malware that sends text messages to a premium number generating large service bills for the user of the targeted device?
正解:
Explanation:
Reference: https://pdfs.semanticscholar.org/7f33/9156f47345bd102c9b05f45f9bfe4c182720.pdf
Question No : 3
Which of the following files provides the most accurate reflection of the device’s date/timestamp related to the last device wipe?
正解:
Question No : 4
Which of the following is a unique 56 bit number assigned to a CDMA handset?
正解:
Explanation:
The Mobile Equipment ID (MEID), also found under the battery cover, is a 56 bit number which replaced the ESN due to the limited number of 32 bit ESN numbers. The MEID is listed in hex, where the first byte is a regional code, next three bytes are a manufacturer code, and remaining three bytes are a manufacturer-assigned serial number. Reference: https://sites.google.com/site/bbayles/index/cdma_hardware_id
Question No : 5
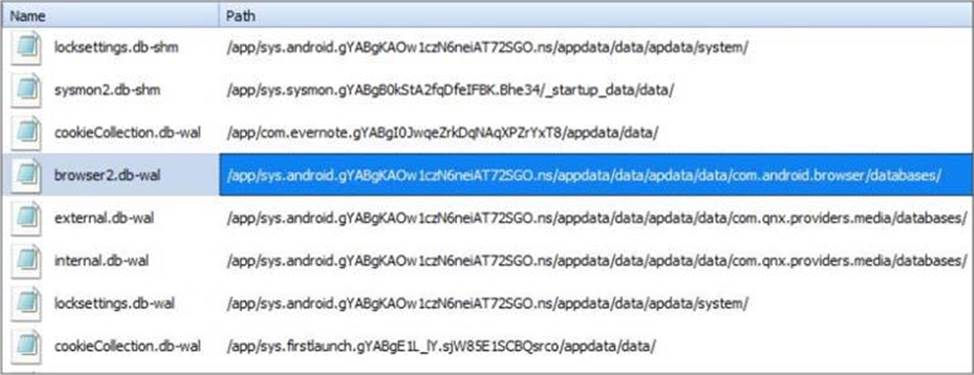
Where can an analyst find data to provide additional artifacts to support the evidence in the highlighted file?
正解:
Question No : 6
The files pictured below from a BlackBerry OS10 file system have a unique file extension.
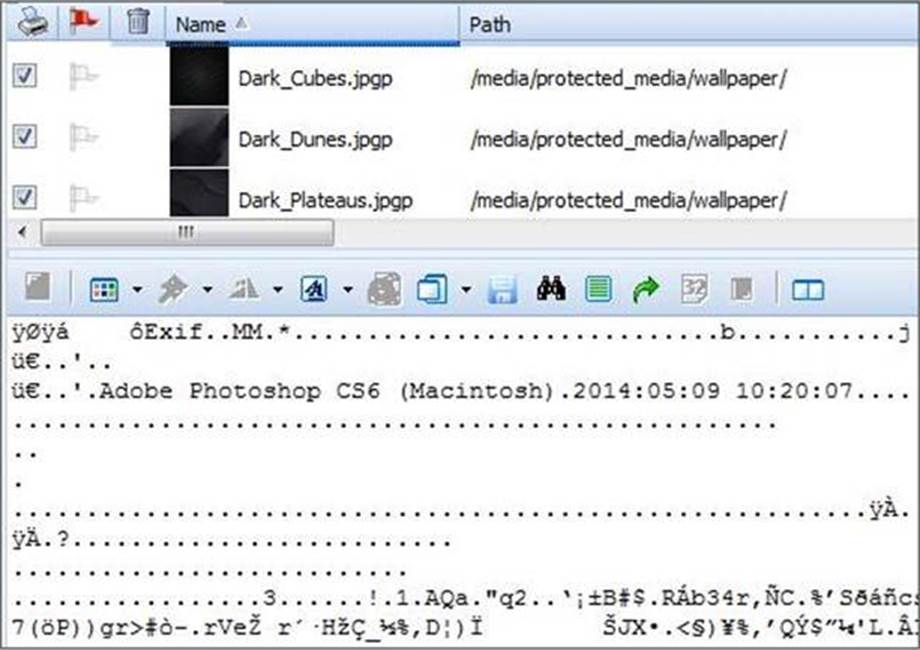
What can be concluded about these files?
正解:
Explanation:
Reference: https://forums.crackberry.com/blackberry-q10-f272/protected-media-911023/
Question No : 7
Physical Analyzer provides a function to narrow down a search based on a timestamp, a type, a party or date.
What is the name of this advanced searching capability?
正解:
Explanation:
Physical Analyzer offers the Timeline feature to narrow down what happened on the smartphone during a specific time, type, party, etc. This is commonly used to narrow down time periods. Data that is manually carved will not be shown here. There is also an option to create a custom timeline specification.
Question No : 8
An Android device user is known to use Facebook to communicate with other parties under examination. There is no evidence of the Facebook application on the phone.
If there was Facebook usage where would an examiner expect to find these artifacts?
正解:
Explanation:
Reference: https://www.ctsforensics.com/assets/news/35550_Web-update.pdf
Question No : 9
In 2015, Apple’s iTunes store was found to be hosting several malicious applications that were infected as a result of hacked version of the developer toolkit used to create applications.
Which Apple developer suite was targeted?
正解:
Explanation:
Reference: http://money.cnn.com/2015/09/21/technology/apple-xcode-hack/index.html
Question No : 10
Which of the following is required in addition to the Apple ID of the custodian to access IOS backup files that are stored in ICloud?
正解:
Question No : 11
Cellebrite Physical Analyzer uses Bit Defender to scan for malware by flagging files who have known bad hash values.
This is an example of which type of mobile malware detection?
正解:
Explanation:
Reference: https://security.stackexchange.com/questions/95186/what-is-the-precise-difference-between-asignature-based-vs-behavior-based-antiv
Question No : 12
When conducting forensic analysis of an associated media card, one would most often expect to find this particular file system format?
正解:
Question No : 13
Which artifact must be carved out manually when examining a file system acquisition of an Android device?
正解:
Question No : 14
As part of your analysis of a legacy BlackBerry device, you examine the installed applications list and it appears that no third-party applications were installed on the device.
Which other file may provide you with additional information on applications that were accessed with the handset?
正解:
Explanation:
Analyzing both the Event Logs (which are accessible in Oxygen Forensic Suite) and/or the Installed Applications (which is a feature available in Cellebrite Physical Analyzer) may lead you to additional data. If applications of interest were located in the Event Logs, a Keyword Search across the media may reveal more data related to the application.
Question No : 15
An analyst investigating a Nokia S60 Symbian device wants to know if an Adobe Flash file on the handset is compromised.
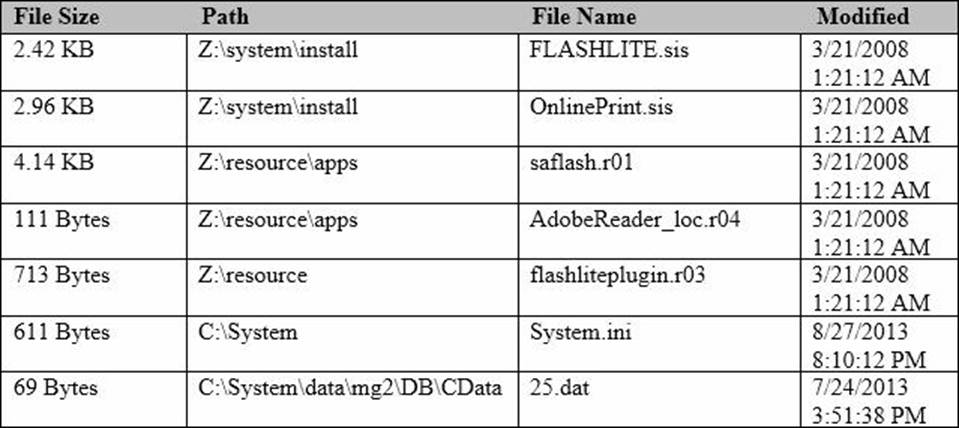
Which file in the image will best target the Adobe Flash files?
正解:
Explanation:
A sis.file is the package that Symbian uses to install applications on their OS compatible handsets. Knowing that you are investigating an application that is installed on the handset, first narrowing the files down to installer packages, or *.sis files, is a good starting point. Flash is an Adobe product making the most logical of the two remaining* .sis files for review, the FLASHLITE installer package. There are several other files related to “Flash” but as resource files, they provide supporting documentation and will not contain the .app file or code that was possibly malicious.