IT認証試験問題集
GOWUKAKU|IT認定資格の最新の試験問題集(PDF版・無料サンプル問題)を提供しています
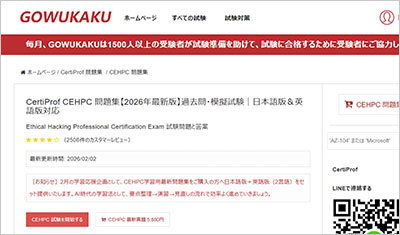
 ホームページ / CertiProf 問題集  / CEHPC 問題集

CertiProf CEHPC 問題集 練習問題・模擬試験|日本語版&英語版対応

Ethical Hacking Professional Certification Exam 試験問題と答案

(0件のカスタマーレビュー)

最終更新日: 2026/10/16  収録内容確認済 | PDF問題集: 全 112 問収録

CEHPC試験対策の学習資料(PDF版:日本語・英語2言語セット)|1年間(365日)無料アップデート付
CEHPC 試験を開始する   
cehpc_shiken_1
cehpc_shiken_2

CEHPC 問題集 仕様・サポート案内

対象試験 CertiProf CEHPC — Ethical Hacking Professional Certification Exam
収録問題数 全 112 問(解答付き/オンライン無料サンプル 50 問公開中)
提供形式・言語 PDF版(日本語版・英語版の2言語セット)
販売価格(税込) 6,880円(税込) ※1回払いの買い切り商品です。自動更新や追加請求はありません。
引き渡し・有効期間 決済完了後すぐにダウンロード可能(日本語版が準備中の科目は、英語版を即時ダウンロードのうえ、日本語版は準備完了次第ご登録メールへ自動送付・有効化されます)。ご購入日から1年間(365日間)無料アップデート対応(期間内の更新版も追加料金なしでダウンロード可能)。
お問い合わせ窓口 メールサポート:[email protected](注文確認・再送・教材に関するご質問|返金・交換条件)

CEHPC サンプル問題プレビュー(抜粋)

収録内容から抜粋したサンプル問題です。「解答・解説を表示」をクリックすると正解を確認できます。

サンプル問題 1: Who uses Metasploit?

  • A: Agricultural engineers.
  • B: Food engineers.
  • C: Cybersecurity experts.
正解:C
Explanation: Metasploit is a widely used penetration testing framework designed to develop, test, and execute exploit code against target systems. It is primarily used by cybersecurity experts, including ethical hackers, penetration testers, red team members, and security researchers. Therefore, option C is the correct answer. In the context of ethical hacking, Metasploit is most commonly used during the exploitation and post-exploitation phases of penetration testing. After reconnaissance and vulnerability scanning identify potential weaknesses, Metasploit allows security professionals to safely verify whether those vulnerabilities can be exploited in real-world scenarios. This helps organizations understand the actual risk level of discovered flaws rather than relying solely on theoretical vulnerability reports. Metasploit provides a vast library of exploits, payloads, auxiliary modules, and post-exploitation tools. Ethical hackers use these modules in controlled environments and with proper authorization to test system defenses, validate security controls, and demonstrate attack paths to stakeholders. It is not designed for non-technical professions such as agriculture or food engineering, making options A and B incorrect. From an ethical standpoint, Metasploit supports defensive security objectives by enabling organizations to identify weaknesses before malicious attackers do. It is frequently used in security assessments, red team exercises, and cybersecurity training programs. When used legally and responsibly, Metasploit helps improve system hardening, incident response readiness, and overall organizational security posture.

サンプル問題 2: Which of the following was a famous hacktivist group?

  • A: Anonymous
  • B: Fan7a5ma
  • C: Hackers
正解:A
Explanation: Anonymous is one of the most well-known and influential hacktivist groups in the history of cybersecurity, making option A the correct answer. Hacktivism refers to the use of hacking techniques to promote political, social, or ideological causes. Understanding hacktivist movements is important when studying current security trends, as these groups have significantly influenced cyber threat landscapes. Anonymous is characterized as a decentralized collective, meaning it has no formal leadership or membership structure. Its activities have included distributed denial-of-service (DDoS) attacks, website defacements, data leaks, and online campaigns targeting governments, corporations, and organizations perceived to be unethical or oppressive. These actions have brought global attention to issues such as censorship, privacy, corruption, and human rights. Option B, “Fan7a5ma,” is not a widely recognized or historically significant hacktivist group, and option C, “Hackers,” is a generic term that describes individuals with technical skills rather than an organized hacktivist collective. Therefore, both are incorrect. From an ethical hacking and defensive security perspective, studying groups like Anonymous helps organizations understand non-financially motivated threats. Hacktivist attacks often aim for public exposure, reputational damage, or service disruption rather than direct monetary gain. This requires different defensive strategies, including improved incident response, public communication planning, and monitoring of geopolitical and social developments that may trigger cyber campaigns. Understanding hacktivist behavior is essential for modern cybersecurity professionals to anticipate emerging threats and strengthen organizational resilience.

サンプル問題 3: What tool would you use to search for hidden directories or files?

  • A: Dirb
  • B: Shodan
  • C: Ping
正解:A
Explanation: DIRB is a specialized web content scanning tool used in ethical hacking and penetration testing to discover hidden directories and files on web servers. It operates by performing a dictionary-based brute-force attack against a target website, attempting to access directories and files that are not publicly linked but may still be accessible. This makes option A the correct answer. DIRB is typically used during the web application reconnaissance and enumeration phases of penetration testing. Ethical hackers rely on it to uncover misconfigurations such as exposed admin panels, backup files, configuration files, or outdated directories that could lead to further compromise. These hidden resources often exist due to poor security practices or improper cleanup during development. Option B, Shodan, is incorrect because Shodan is a search engine used to discover internet-connected devices and services, not hidden directories within a specific website. Option C, Ping, is also incorrect because it is a network utility used only to test host reachability and does not interact with web servers at the application layer. From a defensive security perspective, DIRB helps organizations identify unnecessary exposure in web environments. Discovering hidden directories allows administrators to remove, restrict, or secure them before attackers exploit them. When used ethically and with authorization, DIRB is a powerful tool for improving web application security and reducing attack surfaces.

CertiProf CEHPC試験の準備に向けた復習資料としてCEHPC問題集を提供しています。Ethical Hacking Professional Certification Exam試験の主要な知識ポイントをカバーしています。ページ上部の「CEHPC 試験を開始する」ボタンからオンライン無料サンプル問題を確認できます。

CEHPC問題集の収録内容と更新状況はどうなっていますか?

答え:現在提供されているCEHPC問題集には、CEHPC試験対策に向けた全112問の練習問題と解答が収録されています。Ethical Hacking Professional Certification Exam試験に向けた復習に利用できます。

CEHPC問題集はいつ更新されますか?

答え:最新の更新日時はページ上部に表示されています。出題範囲の改訂に合わせて、CEHPC問題集は継続的に更新されています。更新では既存の基礎の上に新しい問題や改訂内容が反映されます。

CEHPC問題集を覚えれば試験に合格できるのではないですか?

答え:問題と解答の選択肢をただ覚えるだけでは十分ではありません。基礎知識を学習したうえでCEHPC問題集を練習することを推奨します。背景にある概念を理解しておくことで、応用問題にも対応しやすくなります。

CEHPC問題集に解説は付いていますか?

答え:すべての問題集に練習問題と解答が収録されており、一部のCertiProf科目の設問には解答の下に解説や補足説明が付記されています。理解を深めながら復習を進めるのに役立ちます。

試験の時もCEHPC問題集のようにいくつかの答えを選ぶようにヒントを与えますか?

答え:選択問題では指定された数の選択肢を選びます。単に解答の記号を暗記するのではなく、問題文の意図と各選択肢の内容・解説を理解して学習を進めてください。

どうやってCEHPC問題集を使って復習しますか?

答え:時間の許す限り、内容を理解しながら計画的に復習することをお勧めします。CEHPC問題集の多くの設問と知識ポイントを一度の学習ですべて定着させるのは難しいため、3回に分けて反復する方法が効果的です。1回目は全体を通して解説とあわせて理解し、2回目は分野ごとに自分の言葉で説明できるか確認し、3回目は試験直前に間違えやすい設問を中心に総復習します。

学習時間が限られている場合は、CEHPC問題集の選択問題を中心に重要キーワードと正答の根拠を優先して整理してください。また、ドラッグ&ドロップ問題やシミュレーション形式の設問については、手順や前提条件を含めて仕組みを理解しておくことが重要です。

アップデートおよび返金ポリシーについて

1年間の無料アップデート
ご購入日から1年間(365日間)は、CEHPC問題集の更新版を追加料金なしでマイページからダウンロードいただけます。

返金ポリシー
返金の条件は返金ポリシーに従います。具体的なお手続きについては、ご注文情報をご用意のうえ、サポート窓口までご連絡ください。

コメントを残す

採点

CertiProf
I27001F 問題集