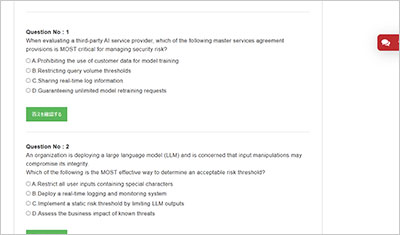
サンプル問題 1: A financial institution plans to deploy an AI system to provide credit risk assessments for loan applications. Which of the following should be given the HIGHEST priority in the system’s design to ensure ethical decision-making and prevent bias?
A: Regularly update the model with new customer data to improve prediction accuracy.
B: Integrate a mechanism for customers to appeal decisions directly within the system.
C: Train the system to provide advisory outputs with final decisions made by human experts.
D: Restrict the model’s decision-making criteria to objective financial metrics only.
正解:C
Explanation: In AI governance frameworks, credit scoring is treated as a high-risk application. For such systems, the highest-priority safeguard is human oversight to ensure fairness, accountability, and prevention of bias in automated decisions. The AI Security Management™ (AAISM) domain of AI Governance and Program Management emphasizes that high-impact AI systems require explicit governance structures and human accountability. Human-in-the-loop design ensures that final decisions remain the responsibility of human experts rather than being fully automated. This is particularly critical in financial contexts, where biased outputs can affect individuals’ access to credit and create compliance risks. Official ISACA AI governance guidance specifies: High-risk AI systems must comply with strict requirements, including human oversight, transparency, and fairness. The purpose of human oversight is to reduce risks to fundamental rights by ensuring humans can intervene or override an automated decision. Bias controls are strengthened by requiring human review processes that can analyze outputs and prevent unfair discrimination. Why other options are not the highest priority: A. Regular updates improve accuracy but do not guarantee fairness or ethical decision-making. Model drift can introduce new bias if not governed properly. B. Appeals mechanisms are important for accountability, but they operate after harm has occurred. Governance frameworks emphasize prevention through human oversight in the decision loop. D. Restricting criteria to “objective metrics” is insufficient, as even objective data can contain hidden proxies for protected attributes. Bias mitigation requires monitoring, testing, and human oversight, not only feature restriction. AAISM Domain Alignment: Domain 1 C AI Governance and Program Management: Ensures accountability, ethical oversight, and governance structures. Domain 2 C AI Risk Management: Identifies and mitigates risks such as bias, discrimination, and lack of transparency. Domain 3 C AI Technologies and Controls: Provides the technical enablers for implementing oversight mechanisms and bias detection tools. Reference from AAISM and ISACA materials: AAISM Exam Content Outline C Domain 1: AI Governance and Program Management (roles, responsibilities, oversight). ISACA AI Governance Guidance (human oversight as mandatory in high-risk AI applications). Bias and Fairness Controls in AI (human review and intervention as a primary safeguard)
サンプル問題 2: A retail organization implements an AI-driven recommendation system that utilizes customer purchase history. Which of the following is the BEST way for the organization to ensure privacy and comply with regulatory standards?
A: Conducting quarterly retraining of the AI model to maintain the accuracy of recommendations
B: Maintaining a register of legal and regulatory requirements for privacy
C: Establishing a governance committee to oversee AI privacy practices
D: Storing customer data indefinitely to ensure the AI model has a complete history
正解:B
Explanation: According to the AI Security Management™ (AAISM) study framework, compliance with privacy and regulatory standards must begin with a formalized process of identifying, documenting, and maintaining applicable obligations. The guidance explicitly notes that organizations should maintain a comprehensive register of legal and regulatory requirements to ensure accountability and alignment with privacy laws. This register serves as the foundation for all governance, risk, and control practices surrounding AI systems that handle personal data. Maintaining such a register ensures that the recommendation system operates under the principles of privacy by design and privacy by default. It allows decision-makers and auditors to trace every AI data processing activity back to relevant compliance obligations, thereby demonstrating adherence to laws such as GDPR, CCPA, or other jurisdictional mandates. Other measures listed in the options contribute to good practice but do not achieve the same direct compliance outcome. Retraining models improves technical accuracy but does not address legal obligations. Oversight committees are valuable but require the documented register as a baseline to oversee effectively. Indefinite storage of customer data contradicts regulatory requirements, particularly the principle of data minimization and storage limitation. AAISM Domain Alignment: This requirement falls under Domain 1 C AI Governance and Program Management, which emphasizes organizational accountability, policy creation, and maintaining compliance documentation as part of a structured governance program. Reference from AAISM and ISACA materials: AAISM Exam Content Outline C Domain 1: AI Governance and Program Management AI Security Management Study Guide C Privacy and Regulatory Compliance Controls ISACA AI Governance Guidance C Maintaining Registers of Applicable Legal Requirements
サンプル問題 3: An organization is updating its vendor arrangements to facilitate the safe adoption of AI technologies. Which of the following would be the PRIMARY challenge in delivering this initiative?
A: Failure to adequately assess AI risk
B: Inability to sufficiently identify shadow AI within the organization
C: Unwillingness of large AI companies to accept updated terms
D: Insufficient legal team experience with AI
正解:C
Explanation: In the AAISM™ guidance, vendor management for AI adoption highlights that large AI providers often resist contractual changes, particularly when customers seek to impose stricter security, transparency, or ethical obligations. The official study materials emphasize that while organizations must evaluate AI risk and build internal expertise, the primary challenge lies in negotiating acceptable contractual terms with dominant AI vendors who may not be willing to adjust their standardized agreements. This resistance limits the ability of organizations to enforce oversight, bias controls, and compliance requirements contractually. Reference: AAISM Exam Content Outline C AI Risk Management AI Security Management Study Guide C Third-Party and Vendor Risk
ISACA AAISM試験の準備に向けた復習資料としてAAISM問題集を提供しています。ISACA Advanced in AI Security Management Exam試験の主要な知識ポイントをカバーしています。ページ上部の「AAISM 試験を開始する」ボタンからオンライン無料サンプル問題を確認できます。
AAISM問題集の収録内容と更新状況はどうなっていますか?
答え:現在提供されているAAISM問題集には、AAISM試験対策に向けた全90問の練習問題と解答が収録されています。ISACA Advanced in AI Security Management Exam試験に向けた復習に利用できます。